FEATURED PROJECT • SYSETHIC

SysEthic

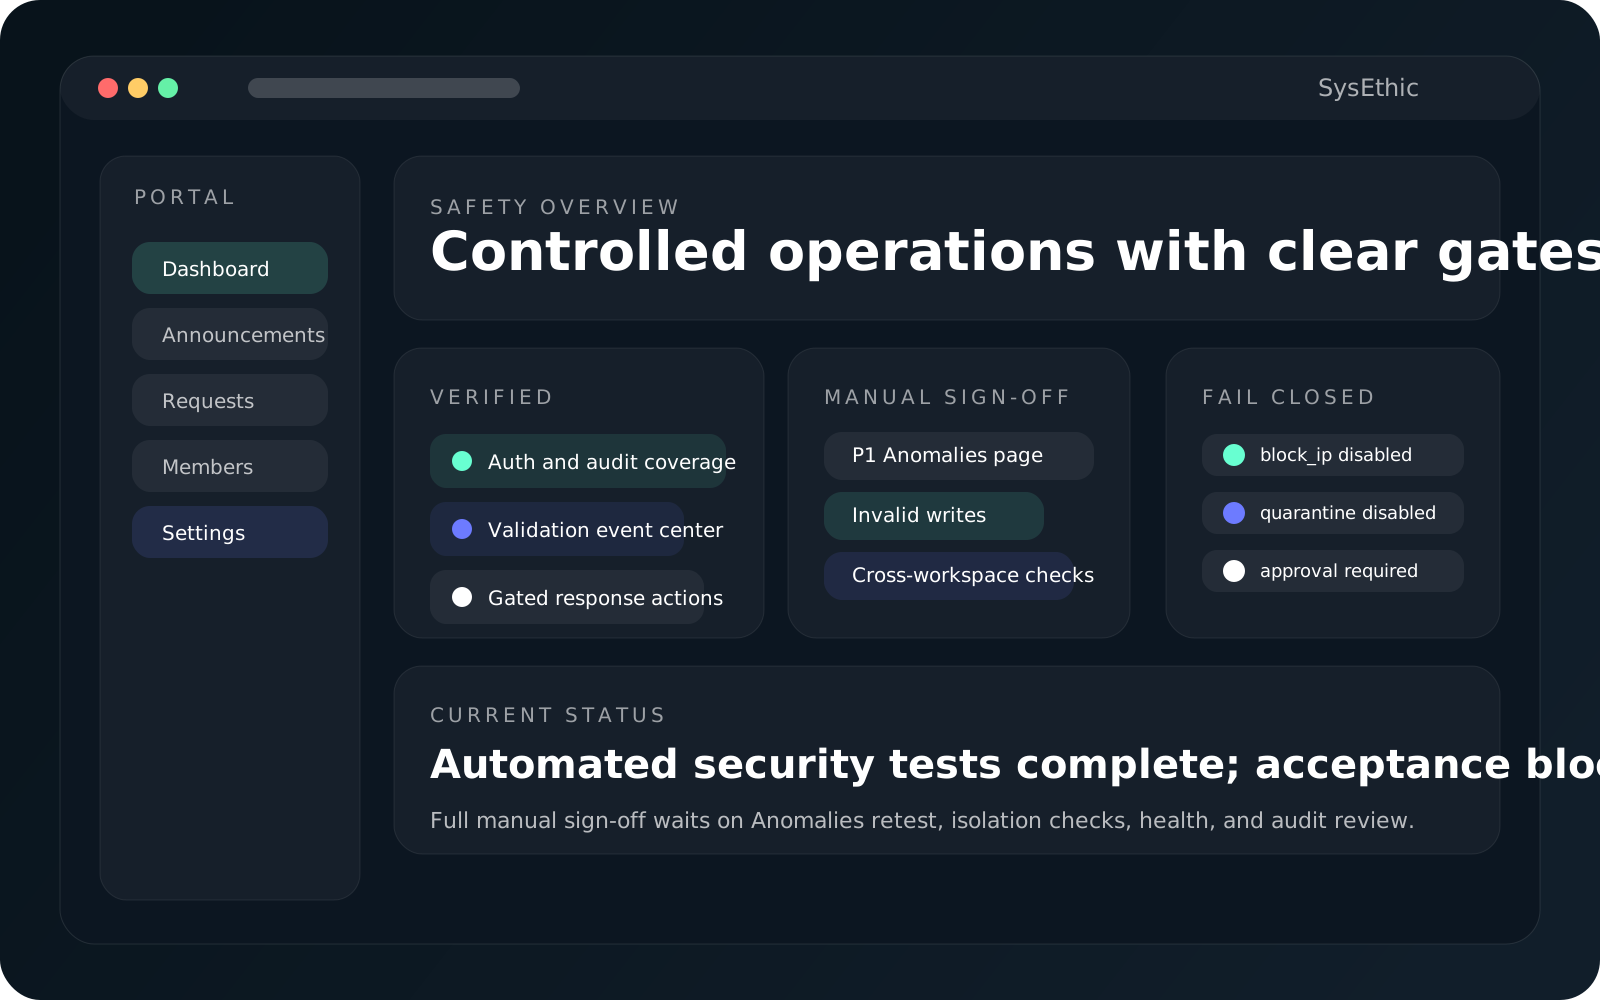
A local security-operations workspace built around authentication, auditability, controlled validation, playbook recommendations, and gated response actions that fail closed when they are not safe to execute.

Phase 5 automated coverage complete Manual sign-off blocked Response actions gated
Role Security workflow, safety controls, and operational QA
Focus Auth, audit trails, validation events, playbooks, and approvals
Surface Dashboard, incidents, validation, audit logs, terminal, and response actions
Status Automated gates complete; full manual sign-off still blocked
Case study

SysEthic milestones and remaining acceptance work.

The page preserves the important distinction between completed automated security coverage and the remaining acceptance failures.

Challenge

Make local response operations safe enough to test.

SysEthic exposes sensitive machine telemetry and diagnostic controls, so identity, storage, audit history, and approval boundaries had to come before broader host-impacting response actions.

Approach

Build the control path before expanding the action surface.

The project added login, durable operational records, normalized audit logs, incident workflows, seeded playbooks, controlled validation events, and manual approvals before enabling any bounded host-impacting action.

Current limit

Automated coverage is complete; manual acceptance still has blockers.

Phase 5 security-critical tests landed on `main`, but full manual sign-off remains blocked by a P1 broken Anomalies page and remaining manual checks for invalid writes, cross-workspace isolation, disabled actions, final health, and audit review.

Verified milestones

  • Phase 3 completed the approval contract and first bounded approved service-restart path.
  • Phase 4 added controlled CPU, memory, network, and sensitive-file validation events that create normal anomalies and incidents.
  • Phase 4 connected validation events to seeded playbooks without bypassing approval-required response actions.
  • Phase 5 added install/startup packaging, health checks, CLI lifecycle commands, and local-only defaults.
  • Phase 5 security-critical coverage was merged with the documented `python -m unittest discover` command.

Remaining acceptance work

  • Blocked: P1 broken Anomalies page requires fix and retest before full manual sign-off.
  • Remaining: invalid automation and anomaly-rule write rejection must be checked manually.
  • Remaining: Acme/Northstar cross-workspace isolation must be checked.
  • Remaining: disabled and unsupported response actions must be checked as fail-closed.
  • Remaining: final health check and audit review must be completed.